QESP. Trust, redefined.
A software-defined cryptographic perimeter that authenticates every device with ephemeral keys that rotate every 3 seconds. No static secrets. No lateral movement. No standing trust.
Engineered to outpace the AI adversary.
Ephemeral Identity
Cryptographic identities are generated, used, and destroyed every 3 seconds. Nothing persists for an attacker to exfiltrate.
Continuous Authentication
Every device, every session, re-authenticates against a dynamic trust fabric. No persistent privilege.
Algorithm-Agnostic Core
A modern cryptographic core that adapts to your stack — drop-in deployment without changing your network or applications.
A four-step trust lifecycle.
Each step in the lifecycle maps directly onto the architecture below — from device enrollment, through ephemeral key generation and per-session authentication, to real-time telemetry on the management console.
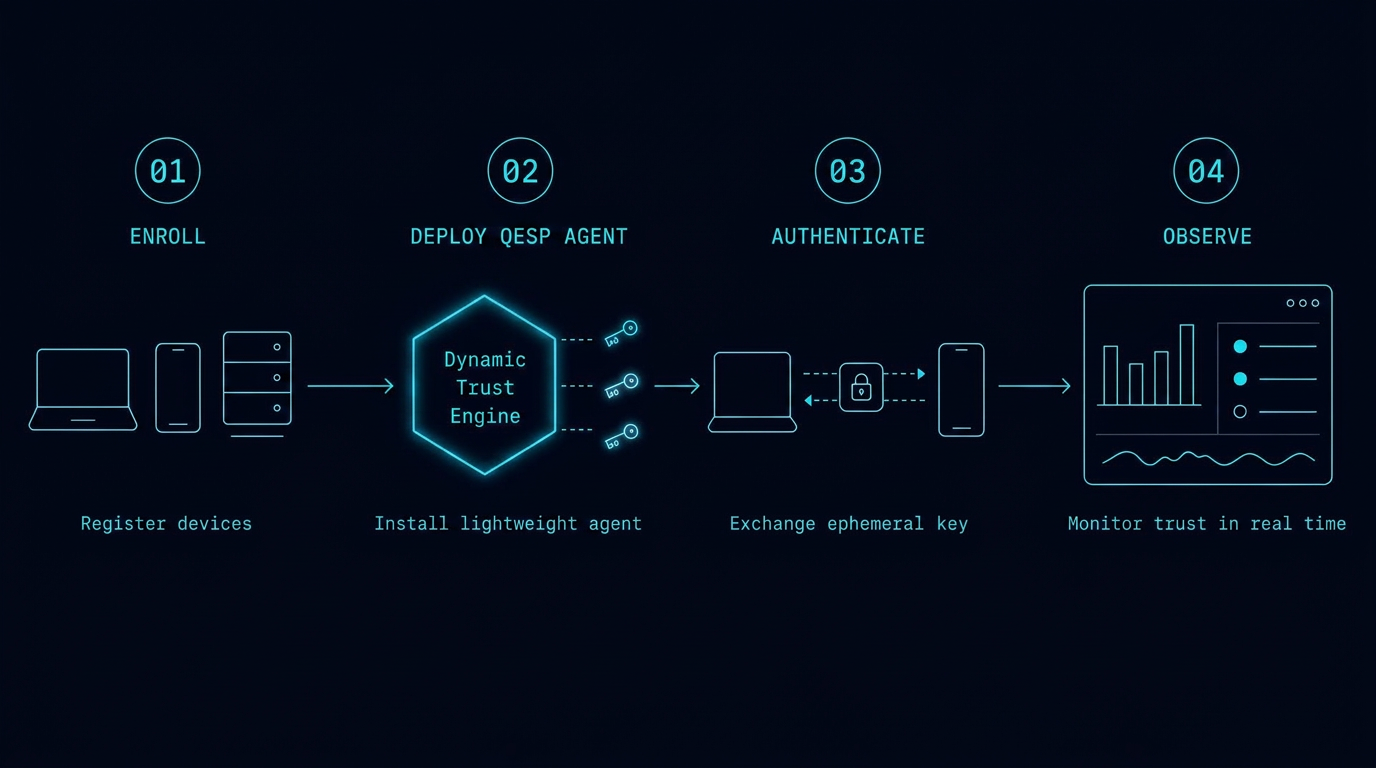
Enroll
Devices register their cryptographic identity to the QESP fabric over a hardened onboarding channel.
Generate
Ephemeral keys are produced on demand by the dynamic trust engine — never stored, never reused.
Authenticate
Every device-to-device session is independently verified with a fresh, single-use credential.
Observe
All trust events stream to the management console for real-time policy and audit.
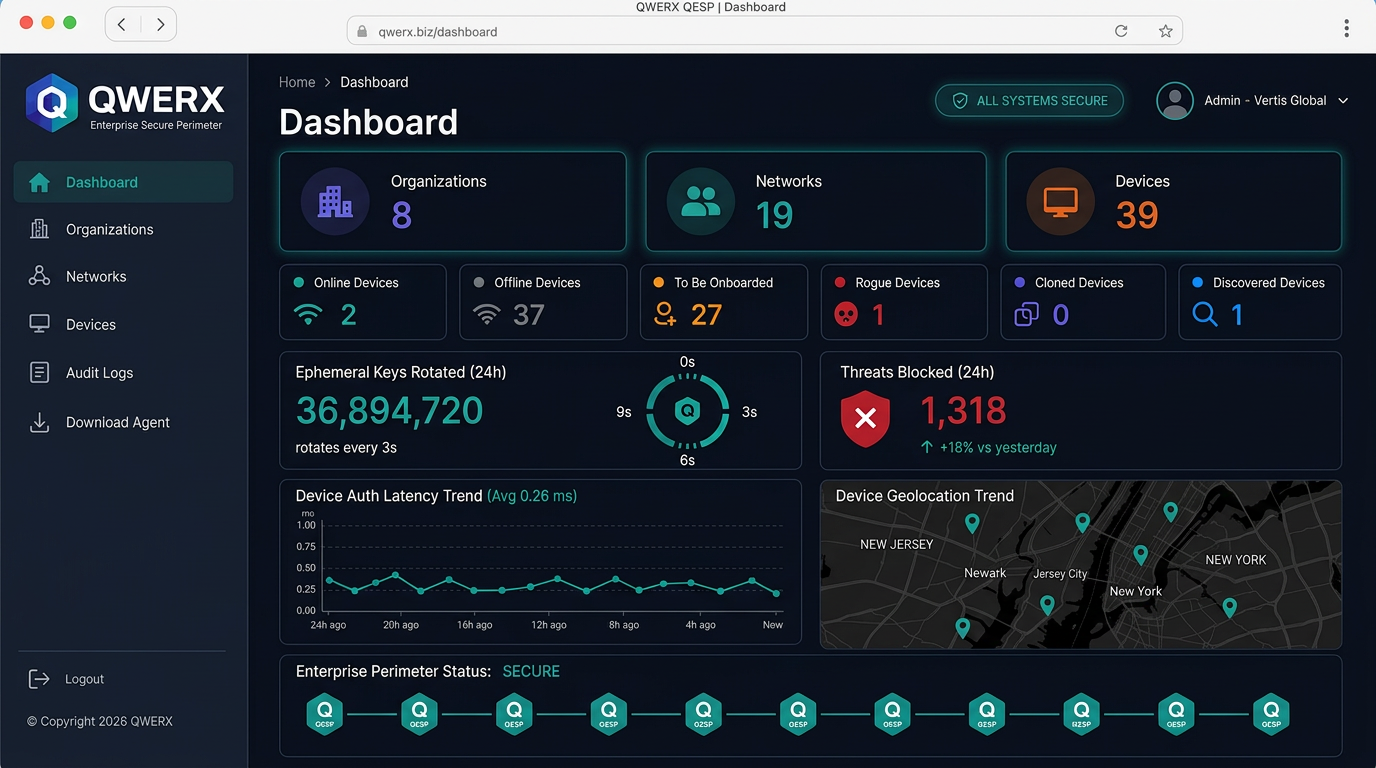
One console. Total dynamic trust.
Real-time observability across every authenticated device, every key generation event, every policy decision — globally distributed, locally enforced.
- Live device fleet posture across global geographies
- Per-session key telemetry and policy event stream
- Drill-down forensics for every authentication decision
- Role-based delegated administration with full audit trail
- API & SIEM integration for SOC workflows
Designed for the threats that broke everyone else.
AI-driven phishing & deepfakes
THREATAdversaries impersonate users and operators with synthetic identities at scale.
QESP: Authentication is bound to device cryptography — there is no human secret to disclose.
Infostealer credential harvesting
THREATMalware exfiltrates passwords, tokens, and cookies from endpoints in seconds.
QESP: Ephemeral keys are useless after 3 seconds — nothing meaningful to steal.
Lateral movement post-compromise
THREATOne foothold cascades into full-network compromise via reused credentials.
QESP: Zero standing trust — every transaction independently re-authenticates.
Standing-credential persistence
THREATLong-lived keys, certificates, and passwords give attackers months of dwell time.
QESP: Every credential is born and erased within a 3-second window.
Supply chain key implant
THREATBackdoored libraries (XZ-style) target long-lived SSH and TLS host keys.
QESP: Authentication is decoupled from static host keys — implants find no anchor.
Session hijack & token replay
THREATStolen session tokens grant adversaries full user privilege.
QESP: Single-use ephemeral credentials cannot be replayed by definition.
Enterprise-grade. Mission-ready.
Cryptography
- ›Algorithm-agnostic core
- ›Modern primitives
- ›Hardware root-of-trust optional
Deployment
- ›Cloud, on-prem, or air-gap
- ›Container & VM packaging
- ›Edge & tactical footprints
- ›Existing PKI co-existence
Operations
- ›Real-time trust telemetry
- ›SIEM/SOAR integrations
- ›Role-based admin
- ›Full audit trail
Identity
- ›Device-bound identity
- ›Per-session credentials
- ›Federated trust domains
- ›Continuous re-authentication
Performance
- ›3-second key regeneration
- ›Linear scale to 100k+ nodes
- ›Low-latency edge enforcement
- ›Bandwidth-efficient
Compliance
- ›Zero-trust architecture aligned
- ›Continuous compliance evidence
- ›Policy-as-code controls
- ›Auditable per-session forensics
See QESP defend a live network.
30-minute technical briefing with our cryptography team. NDA-ready.